24/7 SOC · SIEM / SOC
The control room that sees the attack
before it reaches you.
Our control room alerts in real time on security events and attacks against critical systems. Immediate response is what stops an incident from becoming operational and financial damage.
The console
What an analyst sees.
The alert queue, event volume and the attack path of a live incident — recorded from the console the SOC actually works in.
The data in this recording was replaced. The layout, the timings and the fields are the real console’s.
Three tiers
A centre that works in three critical tiers.
- 1
Tier 1 + Tier 2 — continuous monitoring
24/7 monitoring by analysts holding a broad, current intelligence picture, with real-time alerting.
- 2
Tier 3 — investigation and forensics
Deep forensics on any suspected attack, through to full identification of the attack vector.
- 3
IRT — immediate response team
Attack confirmed? The intervention team moves in to stop it and re-establish a safe working environment.
- 4
Support and lessons learned
We stay with long-running incidents, are experienced in negotiation events, and turn every incident into preventive recommendations.
The service includes
What the service includes.
- 01
Continuous 24/7/365 monitoring
Analysts watch the organisation’s events continuously, not only in office hours.
- 02
Real-time alerting
Detection and alerting on an event in critical systems the moment it happens.
- 03
Investigation and forensics
Tier 3 runs deep forensics to establish how the attack was carried out, and from where.
- 04
Stopping the attack
The IRT moves in to halt the attack and return a safe working environment.
- 05
Preventive recommendations
The investigation comes back as a change to the controls, not only as a document.
- 06
Complex incident support
Including long-running incidents and negotiation events with attackers.
INCIDENT REPLAY · IR-2026-0412
One night in the control room.
A log extract from a ransomware incident stopped before it spread.
- DETECT EDR: anomalous LSASS memory access by svc_backup on FIN-SRV-04
- ALERT SIEM: three failed logons then one success from 10.4.19.77 — out of pattern
- ACTION Tier 1 escalates to Tier 3. Incident IR-2026-0412 opened.
- CRITICAL File-encryption behaviour on FILES01\finance — 147 files touched
- ACTION Network isolation applied to FIN-SRV-04 and FILES01 from the console
- ACTION Three accounts force-reset; every session revoked
- ACTION C2 domain cdn-update-check[.]net blocked at the perimeter
- CONTAINED Encryption stopped. All 147 files restored from the 23:00 snapshot.
- CONTAINED Root cause: a VPN account with no MFA. Report delivered to the customer.
A real incident at one of our customers, published with their consent. Identifying details were changed; the timings were not.
MITRE ATT&CK
What we actually detect.
Our detection coverage, mapped to tactics and techniques. What is still on the roadmap is marked as such — which is exactly what makes the rest worth believing.
- Full coverage
- Partial coverage
- On the roadmap
Initial Access
PhishingValid AccountsExternal Remote ServicesSupply ChainExecution
PowerShellWMIScheduled TaskContainer AdminPersistence
Registry Run KeysCreate AccountBoot AutostartBITS JobsPrivilege Escalation
Token ManipulationBypass UACExploit for PEDefense Evasion
Clear Event LogsImpair DefensesObfuscationRootkitCredential Access
LSASS MemoryBrute ForceKeyloggingKerberoastingLateral Movement
RDPSMB SharesSSHPass-the-HashExfiltration
Exfil over C2Cloud StoragePhysical MediaImpact
Data EncryptedInhibit RecoveryService StopDefacementCoverage is reviewed and updated quarterly, and reported to the customer as part of the monthly review.
Intelligence
A broad, current intelligence picture.
The analysts work against a threat picture that keeps updating: active campaigns, attacker tooling and tradecraft, and the indicators that show up at other customers.
What is caught at one organisation defends all the others.
What happens when an attack is detected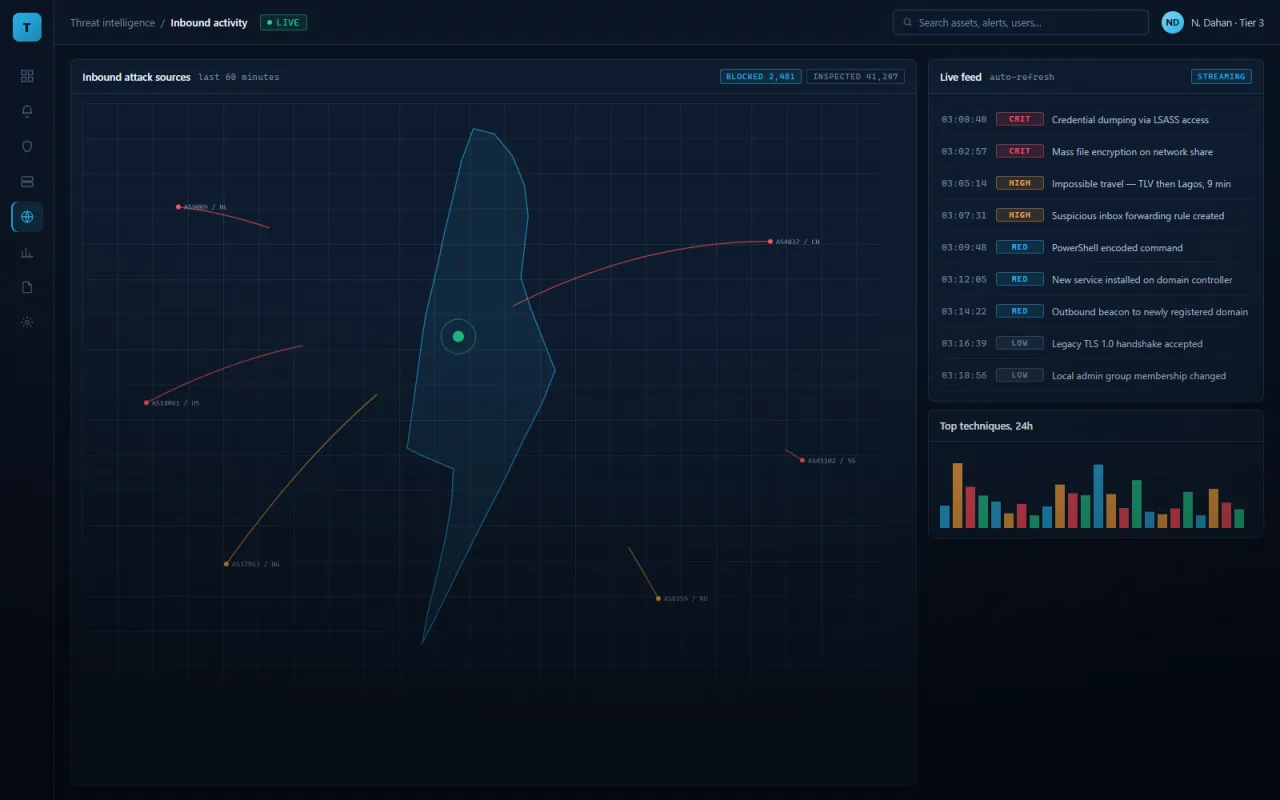
Emergency line · 24/7/365
Under attack?
Do not shut anything down. Call.
Shutting a machine down wipes volatile memory — and part of the evidence with it. Disconnect from the network if you can, delete nothing, and call. A senior analyst is on the line within 15 minutes, customer or not.
08-691-4954