Managed protection · small and mid-sized business
Multi-layered protection —
with no security department.
Most insurers have made a security standard a condition of covering a business at all, and law firms, accountants, medical practices and small businesses are required to manage security to strict standards. Our small and mid-sized business unit is, in practice, the business’s outsourced security unit.
One provider
Three layers, one provider, one invoice.
Email, endpoints and mobile are the three routes almost every attack on a small business takes.
Instead of three products from three vendors, none of which is looking at the others — one managed layer, watched from the same control room that watches large organisations.
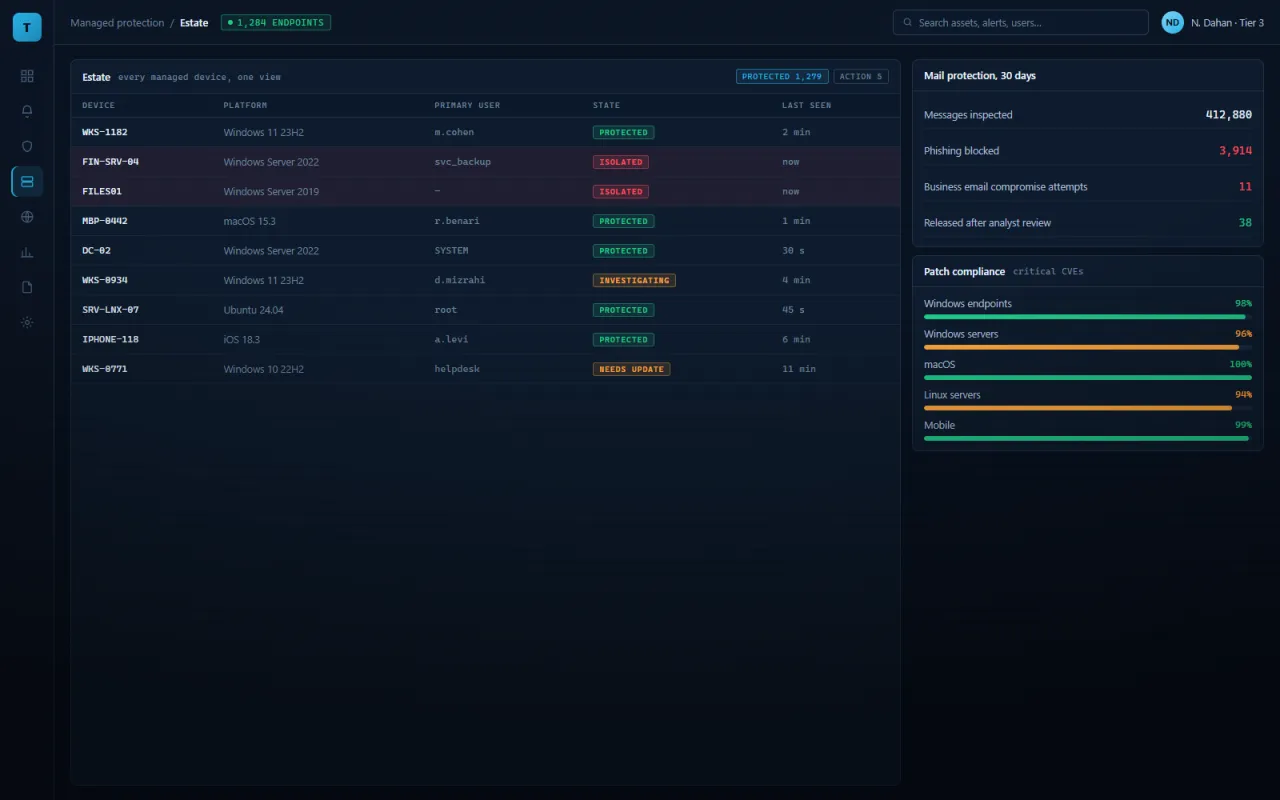
What is in the package
Everything the insurer asks for. In one place.
- 01
Email protection
Filtering phishing, impersonation and CEO fraud — the first vector in almost every incident.
- 02
Endpoint protection
EDR on workstations and servers, with remote isolation the moment something suspicious appears.
- 03
Mobile devices
Protection for phones and tablets that reach company mail and data.
- 04
Identity and access
MFA enforcement, finding compromised service accounts, and watching for unusual logons.
- 05
Monitored from the SOC
The same control room, the same analysts, the same 24/7 — for a business with 30 staff.
- 06
A monthly report
What was blocked, what was checked, what needs fixing. A document you can show an insurer.
The decision
Three ways to defend an organisation.
Written from the point of view of somebody who has to decide, not of a vendor who has to sell.
| TripleCyber | In-house team | General IT provider | |
|---|---|---|---|
| Monitoring at night and at weekends | ✓ | On-call dependent | — |
| A response team that turns up | ✓ | Usually not | — |
| Forensics and root-cause analysis | ✓ | Rare | — |
| Mapping to MITRE ATT&CK | ✓ | Tooling dependent | — |
| Reporting for a regulator or insurer | ✓ | Depends | — |
| Time to stand up | Weeks | Months to a year | Days |
| Cost to start | A monthly package | 3–6 salaries | Low |
"General IT provider" is not a criticism — they were simply not built for this, exactly as we were not built to fix a printer.
Standards, regulation and insurance
Meeting the requirements. With paperwork.
- 01
ISO/IEC 27001
Building the control set and running the programme through to certification.
- 02
Privacy regulation
Data inventory, access control and breach-notification procedure.
- 03
Israeli national cyber doctrine
Applying the defence principles recommended to Israeli organisations.
- 04
Insurer requirements
Assessment, plan and controls — through to the standard the policy demands.
- 05
Hazardous-materials standards
Meeting the requirements specific to regulated sites.
- 06
Supply-chain security
Supplier review, contractual requirements and ongoing assurance.
Frequently asked
How many staff is this for?
The unit is built for organisations up to roughly 100 people. Above that, pairing it with the full SOC usually fits better.
How long does it take to deploy?
Days, not months. We start with email and endpoints and move on to identity and mobile.
Is this enough to get cyber insurance?
In most cases it is the baseline the insurer asks for. We also run the assessment and produce the documents the policy requires.
And if an incident happens anyway?
The same control room and the same response team that handle large organisations handle you.
Emergency line · 24/7/365
Under attack?
Do not shut anything down. Call.
Shutting a machine down wipes volatile memory — and part of the evidence with it. Disconnect from the network if you can, delete nothing, and call. A senior analyst is on the line within 15 minutes, customer or not.
08-691-4954