Consulting and readiness
We start with the picture,
not with the technology.
Almost every time, the real gap turns out not to be a missing product but a control nobody enabled, an account nobody closed, or a procedure nobody ever tested. So we start with the assessment, and reach for technology afterwards.
Risk assessment
The assessment that produces a plan.
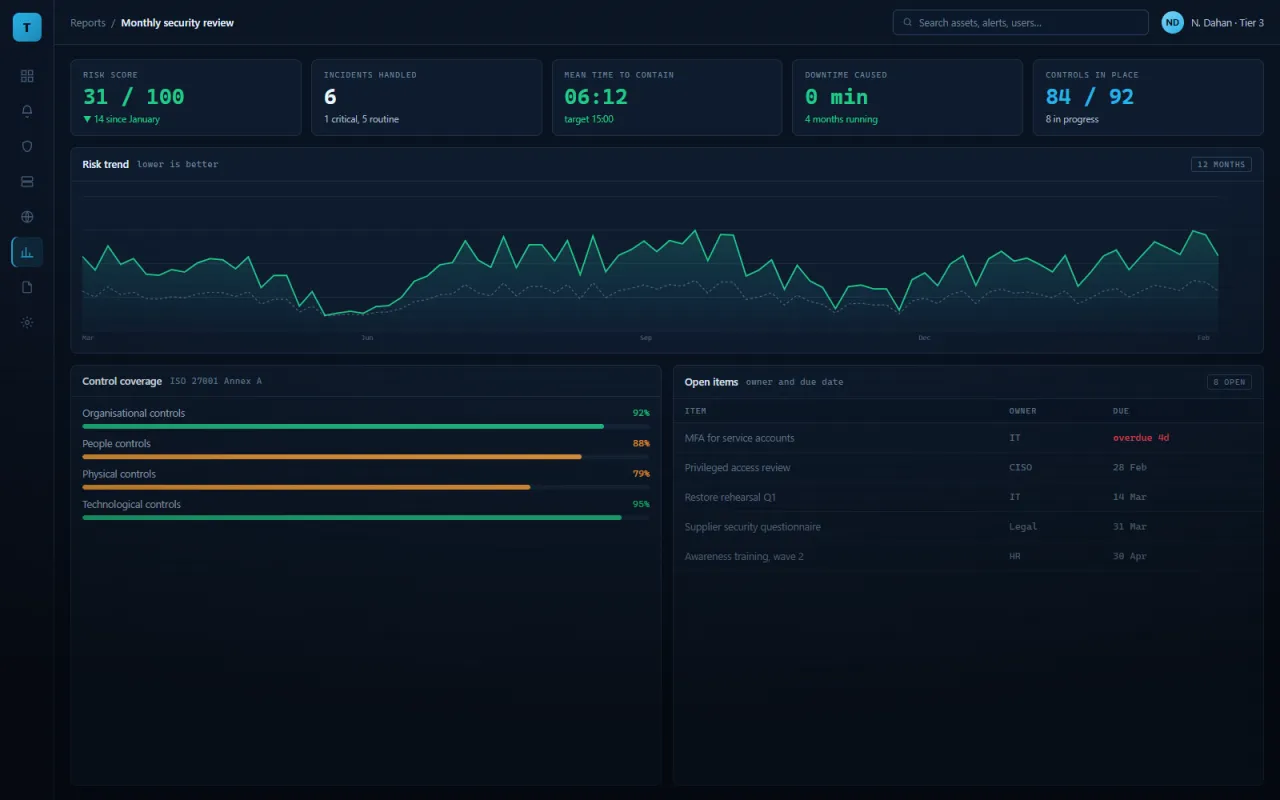
The risk assessment is the main instrument for evaluating security risk and planning whole-estate defence, and it ends in a detailed recommendations document.
The work plan is built on it — ranked by risk, and by what can realistically be done this quarter.
The service includes
From assessment to implementation.
- 01
Risk assessments
A comprehensive evaluation of security risk and a whole-estate defence plan, ending in a detailed recommendations document.
- 02
Regulatory and standards alignment
Cyber defence now has to satisfy steadily stricter standards — including hazardous materials and supply chain.
- 03
Building the work plan
Help building and delivering it alongside the in-house security team: policy, methodology and the right technology.
- 04
CISO as a service
Outsourced security leadership, sized to the organisation, its character and the threats against it.
- 05
Penetration testing
A wide range of tests: mobile, network, external and internal intrusion, vulnerabilities and more.
- 06
Staff training
Training for professionals and staff, including boards, management and the security team itself.
How it runs
Four stages. No shortcuts.
- 1
Risk assessment
A comprehensive assessment of the organisation’s posture and a detailed recommendations document.
- 2
Work plan
A full plan, built alongside the organisation’s own security team.
- 3
Implementation
Policy updates, better methodology and the right technology, deployed.
- 4
Ongoing assurance
Penetration tests, training and continuous review of the defences.
Standards, regulation and insurance
The frameworks we take you to.
- 01
ISO/IEC 27001
Building the control set and running the programme through to certification.
- 02
Privacy regulation
Data inventory, access control and breach-notification procedure.
- 03
Israeli national cyber doctrine
Applying the defence principles recommended to Israeli organisations.
- 04
Insurer requirements
Assessment, plan and controls — through to the standard the policy demands.
- 05
Hazardous-materials standards
Meeting the requirements specific to regulated sites.
- 06
Supply-chain security
Supplier review, contractual requirements and ongoing assurance.
Emergency line · 24/7/365
Under attack?
Do not shut anything down. Call.
Shutting a machine down wipes volatile memory — and part of the evidence with it. Disconnect from the network if you can, delete nothing, and call. A senior analyst is on the line within 15 minutes, customer or not.
08-691-4954