TripleSOC · SIEM / EDR
The platform
behind the control room.
TripleSOC is a complete security platform: telemetry collection from the endpoints, threat detection, automated response playbooks and real-time monitoring — all built on the Triple Enablement cryptographic identity layer.
Operations
From telemetry to action.
Detection is only the beginning. What sets an operational platform apart is the second after: a playbook that runs isolation, revokes sessions, resets credentials and opens an incident — before an analyst has typed a word.
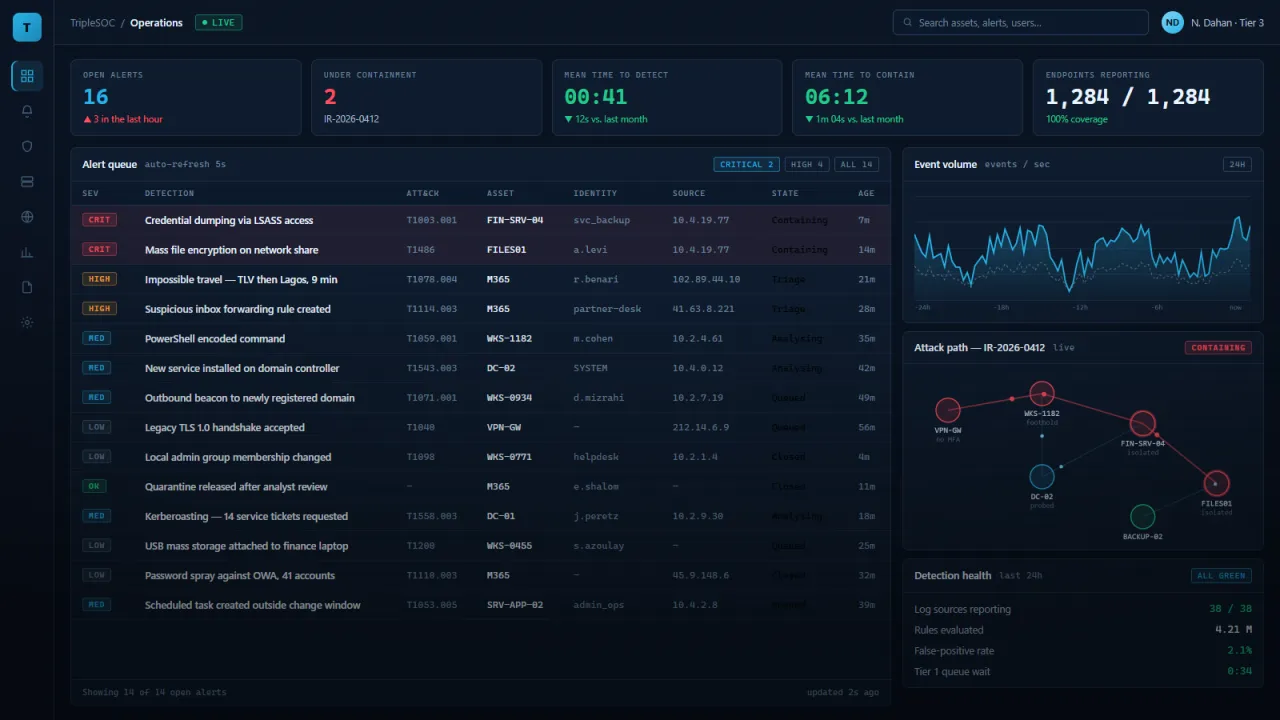
What is in the platform
Six capabilities. One console.
- 01
Telemetry collection
Endpoints, servers, cloud, email and identities — in one place.
- 02
Threat detection
Detection rules mapped to MITRE ATT&CK, with updating threat intelligence.
- 03
Automated playbooks
Immediate response to known scenarios, without waiting for a human.
- 04
Isolation and quarantine
Cut a compromised asset off the network in one click, even when it is not in the office.
- 05
Full operating-system coverage
Windows, macOS, Linux, iOS and Android.
- 06
Compliance reporting
Reports you can submit to a regulator and an insurer.
MITRE ATT&CK
What we actually detect.
Our detection coverage, mapped to tactics and techniques. What is still on the roadmap is marked as such — which is exactly what makes the rest worth believing.
- Full coverage
- Partial coverage
- On the roadmap
Initial Access
PhishingValid AccountsExternal Remote ServicesSupply ChainExecution
PowerShellWMIScheduled TaskContainer AdminPersistence
Registry Run KeysCreate AccountBoot AutostartBITS JobsPrivilege Escalation
Token ManipulationBypass UACExploit for PEDefense Evasion
Clear Event LogsImpair DefensesObfuscationRootkitCredential Access
LSASS MemoryBrute ForceKeyloggingKerberoastingLateral Movement
RDPSMB SharesSSHPass-the-HashExfiltration
Exfil over C2Cloud StoragePhysical MediaImpact
Data EncryptedInhibit RecoveryService StopDefacementCoverage is reviewed and updated quarterly, and reported to the customer as part of the monthly review.
For management
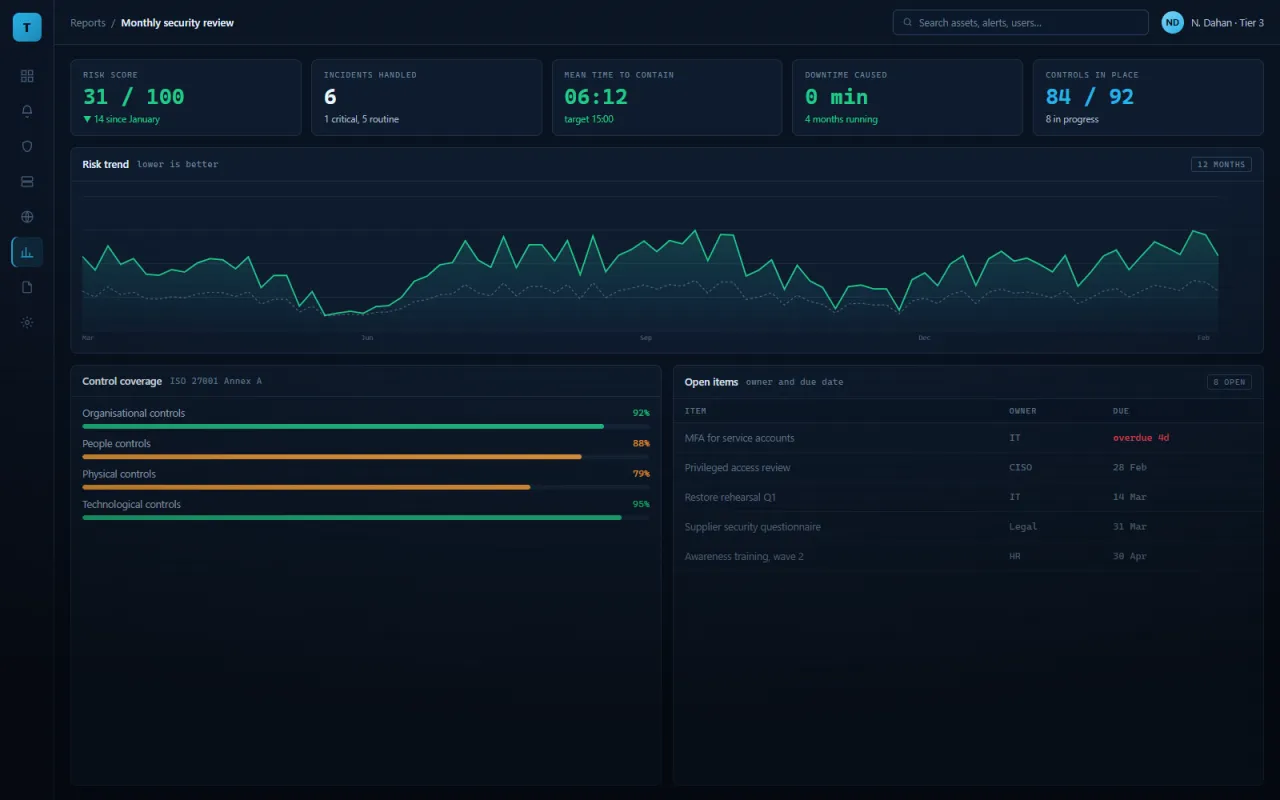
The report as management receives it.
A general manager does not need to see alerts. They need to see the trend, the open risk, and who owns closing it by when.
The monthly review was built for exactly that.
Emergency line · 24/7/365
Under attack?
Do not shut anything down. Call.
Shutting a machine down wipes volatile memory — and part of the evidence with it. Disconnect from the network if you can, delete nothing, and call. A senior analyst is on the line within 15 minutes, customer or not.
08-691-4954